
Published August 27, 2026 · 12 min read · Updated September 27, 2026
Certificate of Data Destruction Requirements for Business IT Assets
A certificate of data destruction holds up only when it ties specific media to a defined method, a verified result and an accountable chain of custody. Here is what a defensible certificate needs to include.
A certificate of data destruction is useful only when it connects a specific service to specific media, a defined method, a verified result and an accountable chain of custody. A one-page statement that “all data was destroyed” may look reassuring, yet it leaves open which assets were included, what happened to media that failed, who did the work, and whether the equipment was recycled or reused afterward.
Modern Waste Solutions has provided data destruction, on-site shredding, electronics recycling, tracking and reports to California organizations since 1999 from its Sacramento facility. The practical lesson from that work: define the certificate fields before service, so the evidence you get back supports audits, customer obligations, insurance reviews and internal governance.
A certificate of data destruction is an attestation that identified media or a defined load completed a specified sanitization or physical destruction service. It is normally issued by an internal authorized function or an external vendor after the work. The certificate should be part of a larger record set that includes authorization, inventory, chain of custody, method details, verification or process evidence, exceptions, and final disposition.
The document is commonly needed when a business retires computers, servers, storage arrays, backup tapes, phones, printers, copiers, medical equipment, network devices, or paper containing protected information. It may support customer contracts, privacy and security programs, cyber-insurance reviews, legal or regulatory audits, asset-management closeout, and vendor oversight. It can also show that media was treated before equipment was reused, sold, donated, returned to a lessor, or recycled.
| Use case | Why a certificate helps | Additional evidence needed |
|---|---|---|
| IT refresh | Closes the retirement workflow | Released asset inventory and reconciliation |
| Customer or contract requirement | Shows the required service occurred | Contract clause, method, and asset scope |
| Healthcare or regulated data | Supports safeguards and final disposition | Policy, BAA/vendor review, custody, exceptions |
| Lease return | Demonstrates media treatment before transfer | Ownership, device list, lessor acceptance |
| On-site shredding | Records witnessed physical destruction | Scan list, operator, location, and witness |
| Facility-based service | Records completion after secure transport | Pickup receipt, receiving reconciliation, and custody |
The certificate is not a substitute for process. It cannot prove that a missing drive was destroyed, that the correct tool was used on an SSD, or that every serial number reached the vendor unless the underlying records support those facts. It also does not automatically establish compliance with every law. The organization remains responsible for choosing a method suitable for the media, information sensitivity, legal duties, and intended disposition.
NIST SP 800-88 Rev. 2 treats documentation as part of a media-sanitization program and distinguishes method execution, verification, validation, and final disposition. A strong certificate reflects those concepts without claiming that NIST itself certified the vendor or the individual transaction.
The certificate should identify who requested the service, who performed it, what media was included, when and where it occurred, what method was used, and what result was obtained. The level of detail should match risk. High-sensitivity or serialized assets generally require asset-level reporting; homogeneous low-risk media may be managed by sealed container, lot, count, or weight if policy permits.
| Field | Status | Purpose |
|---|---|---|
| Client legal name and service location | Required | Identifies the organization and project |
| Vendor legal name and processing location | Required | Identifies the accountable service provider |
| Service date and certificate number | Required | Creates a unique, traceable record |
| Media type and quantity | Required | Defines the population treated |
| Destruction or sanitization method | Required | States what was actually performed |
| Outcome and completion statement | Required | Records the service result |
| Asset tag and serial number | Required when contract/policy calls for serialization | Connects evidence to individual media |
| Standard and version | Recommended or contract-required | Shows the method framework used |
| Verification and validation result | Recommended for NIST-aligned work | Shows technical completion and acceptance |
| Operator and witness | Recommended or required for witnessed work | Establishes accountability |
| Chain-of-custody reference | Recommended | Connects the certificate to transfer events |
| Exception reference | Required when any media failed, was missing, or changed route | Prevents a blanket statement from hiding unresolved items |
| Final disposition | Recommended | States reuse, recycling, return, or other outcome |
| Authorized signature or secure issuance control | Required | Protects record authenticity |
The certificate creation workflow should be controlled. First, reconcile the received assets against the authorized release list. Second, perform the approved method and capture results. Third, separate successful, failed, missing, and exception items. Fourth, validate whether the outcome is acceptable for the intended disposition. Fifth, issue the certificate only for the completed population and link unresolved items to an exception report.
Avoid blank fields, generic “industry standard” descriptions, or ranges that cannot be traced. If serial numbers are unreadable, the report should state how the asset was identified and how the exception was approved. If a drive fails logical sanitization and is later shredded, the final record should show both events and the final accepted outcome.
For computer destruction, distinguish destruction of the storage media from recycling of the chassis. A certificate that lists a computer does not necessarily prove its internal drives were present, inventoried, and destroyed. The intake procedure should record drive count and serial numbers or explain the approved lot-control method.
Certificates are named inconsistently across the recycling and destruction industry. The title matters less than the scope and fields. A business should read what the document actually attests and not assume that “certificate of destruction,” “certificate of recycling,” and “certificate of recycling and destruction” prove the same event.
| Document | What it normally proves | What it may not prove |
|---|---|---|
| Data destruction certificate | Specified media completed an identified destruction or sanitization service | Environmental recycling of equipment and materials |
| E-waste certificate of destruction | A defined electronics load was destroyed or processed under the stated service | Asset-level data sanitization unless methods and identifiers are included |
| Certificate of recycling | Material was accepted or processed for recycling | Data destruction, final material yield, or every downstream destination |
| Certificate of recycling and destruction | Both destruction and recycling occurred within a combined scope | Which components were destroyed versus reused unless itemized |
| Shredding certificate | Media or paper passed through a shredding process | NIST outcome, fragment suitability, or asset completeness without supporting data |
| Computer recycling certificate | Computers entered an electronics recycling route | Treatment of internal drives, batteries, or reusable components |
A certificate of recycling may be sufficient for keyboards, cables, and non-data-bearing peripherals managed by weight. It is usually insufficient for servers or laptops if information security requires proof of media treatment. Conversely, a serialized hard-drive destruction certificate does not show where circuit boards, metals, plastics, and batteries went afterward.
The closeout package can contain multiple documents. A pickup receipt records custody. A receiving report reconciles the load. A sanitization report records logical treatment. A shredding certificate records physical destruction. A recycling certificate records the material service. A downstream summary describes subsequent processors. A settlement shows value recovery and fees. Keeping those records separate can be more transparent than forcing every claim into one certificate.
Businesses should also distinguish device-level from lot-level evidence. A sealed console of paper can be tracked by container ID and weight, while a group of high-risk drives may require serial numbers. The policy should define when each level is acceptable and how the certificate references the underlying list.
During vendor selection, ask for redacted samples of each document type. Confirm whether certificates are generated automatically from scan data, whether changes are logged, who can reissue a document, how long reports remain available, and whether subcontracted processing appears in the final record.
A NIST-aligned certificate should use the current Rev. 2 concepts accurately. It should identify the intended sanitization outcome (Clear, Purge or Destroy) and the technique used for the specific media. It should not state “NIST certified,” because NIST does not issue a universal private-vendor certification for destruction transactions.
The record begins with media identification and method selection. For a magnetic hard disk, a validated overwrite may support Clear, while a supported purge technique, degaussing, or physical destruction may be selected for higher assurance. For an SSD, overwrite may not reach remapped or overprovisioned cells; a supported sanitize command, cryptographic erase under valid prerequisites, or physical destruction may be appropriate. The certificate or attached report should state enough detail to understand the choice. Our NIST 800-88 data wiping and on-site hard drive shredding services each report the method used per drive.
| NIST-aligned element | Certificate or attachment content |
|---|---|
| Media identity | Asset tag, serial number, manufacturer/model, media type, capacity |
| Information/risk decision | Approved outcome or policy reference |
| Technique | Overwrite, cryptographic erase, sanitize command, degauss, shred, or other defined process |
| Tool/equipment | Product, model, version, equipment ID, and relevant settings |
| Execution result | Successful completion, failure, warning, or exception |
| Verification | Check that the technique completed and errors were reviewed |
| Validation | Responsible determination that the result is acceptable for disposition |
| Final disposition | Reuse, return, sale, recycle, or destruction |
Verification and validation should not be collapsed into a vague “passed” field. Verification addresses whether the technique completed as expected. Validation considers whether the result is acceptable given the media, risk, evidence, and intended next use. A tool may report success while the wrong asset was scanned or the encryption prerequisite for cryptographic erase was not met; validation is where those issues are caught.
Failed media must remain visible. If an overwrite fails and the drive is physically destroyed, the record should show the failed attempt, escalation, final method, and accepted outcome. A certificate covering only successful records can create an unexplained difference from the pickup inventory.
The standard version belongs in the record when the organization or contract relies on it. Rev. 2 supersedes Rev. 1, so templates should not silently mix terminology. However, the certificate should avoid reproducing copyrighted standard text or implying endorsement. It should document the organization’s implementation and evidence.
A template is a controlled starting point, not proof that the underlying process occurred. Businesses should customize certificate and policy templates to their asset classes, data risks, legal duties, vendor model, and report systems. The template fields must correspond to data that someone actually captures and verifies.
- Define the scope. Identify locations, business units, media, paper, third parties, and disposition routes covered.
- Map each field to a source. Asset IDs may come from the ITAM system; method results from a sanitization tool; custody events from logistics; certificates from the vendor portal.
- Assign field ownership. State who enters, verifies, approves, and can correct each critical record.
- Control required fields. Prevent certificate issuance when client, date, method, asset scope, result, or authorization is blank.
- Create exception codes. Include missing asset, unreadable serial, failed wipe, unexpected media, damage, rejected load, and route change.
- Protect document integrity. Use unique IDs, controlled issuance, revision history, and access restrictions.
- Test with edge cases. Run the template against a failed SSD, mixed-media lot, on-site witness, lease return, and partial pickup.
| Template risk | Control |
|---|---|
| Blank method or standard | Make fields mandatory and use approved controlled values |
| Copying old client data | Generate from transaction records, not manual duplication |
| Certificate issued before reconciliation | Block issuance until exceptions are resolved or disclosed |
| Unsupported compliance claim | Use factual method and outcome language reviewed by counsel/compliance |
| Missing subcontractor or site | Record actual processing location and responsible entity |
| Unverifiable signature | Use authenticated portal issuance or controlled signature authority |
The data destruction policy template should define authorization and method selection; the certificate template should record a completed event. Do not put policy promises into the certificate if they cannot be demonstrated for the transaction. Similarly, do not use a certificate field as a substitute for a legal-hold release or data-classification decision.
Request the vendor’s sample formats during procurement and include required fields in the contract. If the vendor can provide only a generic load certificate while the business requires serial-level proof, that mismatch should be resolved before assets are transferred.
The final audit package should show a continuous story: the organization authorized disposition, transferred the correct assets, applied the approved method, reviewed results, resolved exceptions, and completed the intended reuse or recycling route. No single document needs to contain every detail, but stable identifiers must connect them.
| Document | Audit purpose |
|---|---|
| Approved release inventory | Defines assets and authorization |
| Legal-hold and ownership signoff | Shows assets were eligible for disposition |
| Chain-of-custody log | Records transfer, transport, receipt, and handling events |
| Sanitization or destruction report | Shows method, result, verification, and exceptions |
| Certificate of data destruction | Attests completion for the defined scope |
| Recycling certificate and downstream record | Supports environmental disposition |
| Exception and corrective-action log | Explains missing, failed, rejected, or rerouted assets |
| Settlement or reuse report | Documents resale, donation, return, or net recovery |
A U.S. data destruction certificate normally addresses a service and the organization’s applicable legal, contractual, and policy context. A “WEEE certificate of destruction” is often used in European electrical and electronic waste contexts, but the label alone does not establish compliance with a specific national WEEE system. For cross-border operations, verify the jurisdiction, waste status, shipment, producer-responsibility, and certificate requirements rather than reusing a U.S. form unchanged.
Practical recommendations are to retain the audit package under a documented schedule, test portal access before an audit, and reconcile certificate totals against the original inventory. Do not close a project while exceptions remain open merely because a certificate was issued.
Add a periodic quality review to the program. Select a sample of completed projects and confirm that the release inventory, custody timestamps, method records, certificates, and recycling outcomes agree. Review any corrected or reissued certificate to ensure the change is authorized, traceable, and does not hide the original exception. Sampling like this is how you find out whether the evidence holds up before an auditor does.
Does a certificate of recycling prove data was destroyed?
No. A certificate of recycling covers the material service. For data-bearing equipment you also need a data destruction record that names the media, the method and the result.
Can a vendor call its certificate “NIST certified”?
No. NIST publishes SP 800-88 as guidance and does not certify vendors or individual destruction jobs. A certificate can state that the method followed NIST SP 800-88 Rev. 2 and name the outcome, such as Purge or Destroy.
Do we need serial numbers on the certificate?
For laptops, servers, drives and other high-risk media, usually yes; serial-level records are what let you match the certificate to your asset inventory. Low-risk material such as cables can be documented by weight or container.
How long should we keep certificates of data destruction?
Follow your records retention schedule and any contract or regulatory requirement that applies to the data. Store the certificate with the pickup inventory and chain-of-custody record so the package stays complete.
Modern Waste Solutions provides secure data destruction and electronic waste recycling with certificates built around your inventory. Tell us before service which serialization, media, method, location, witness, recycling and certificate fields you need, and request a quote so the final package matches your requirements.
- NIST SP 800-88 Rev. 2, Guidelines for Media Sanitization: csrc.nist.gov/pubs/sp/800/88/r2/final
- Modern Waste Solutions: Secure Data Destruction
- Modern Waste Solutions: Electronic Waste Recycling
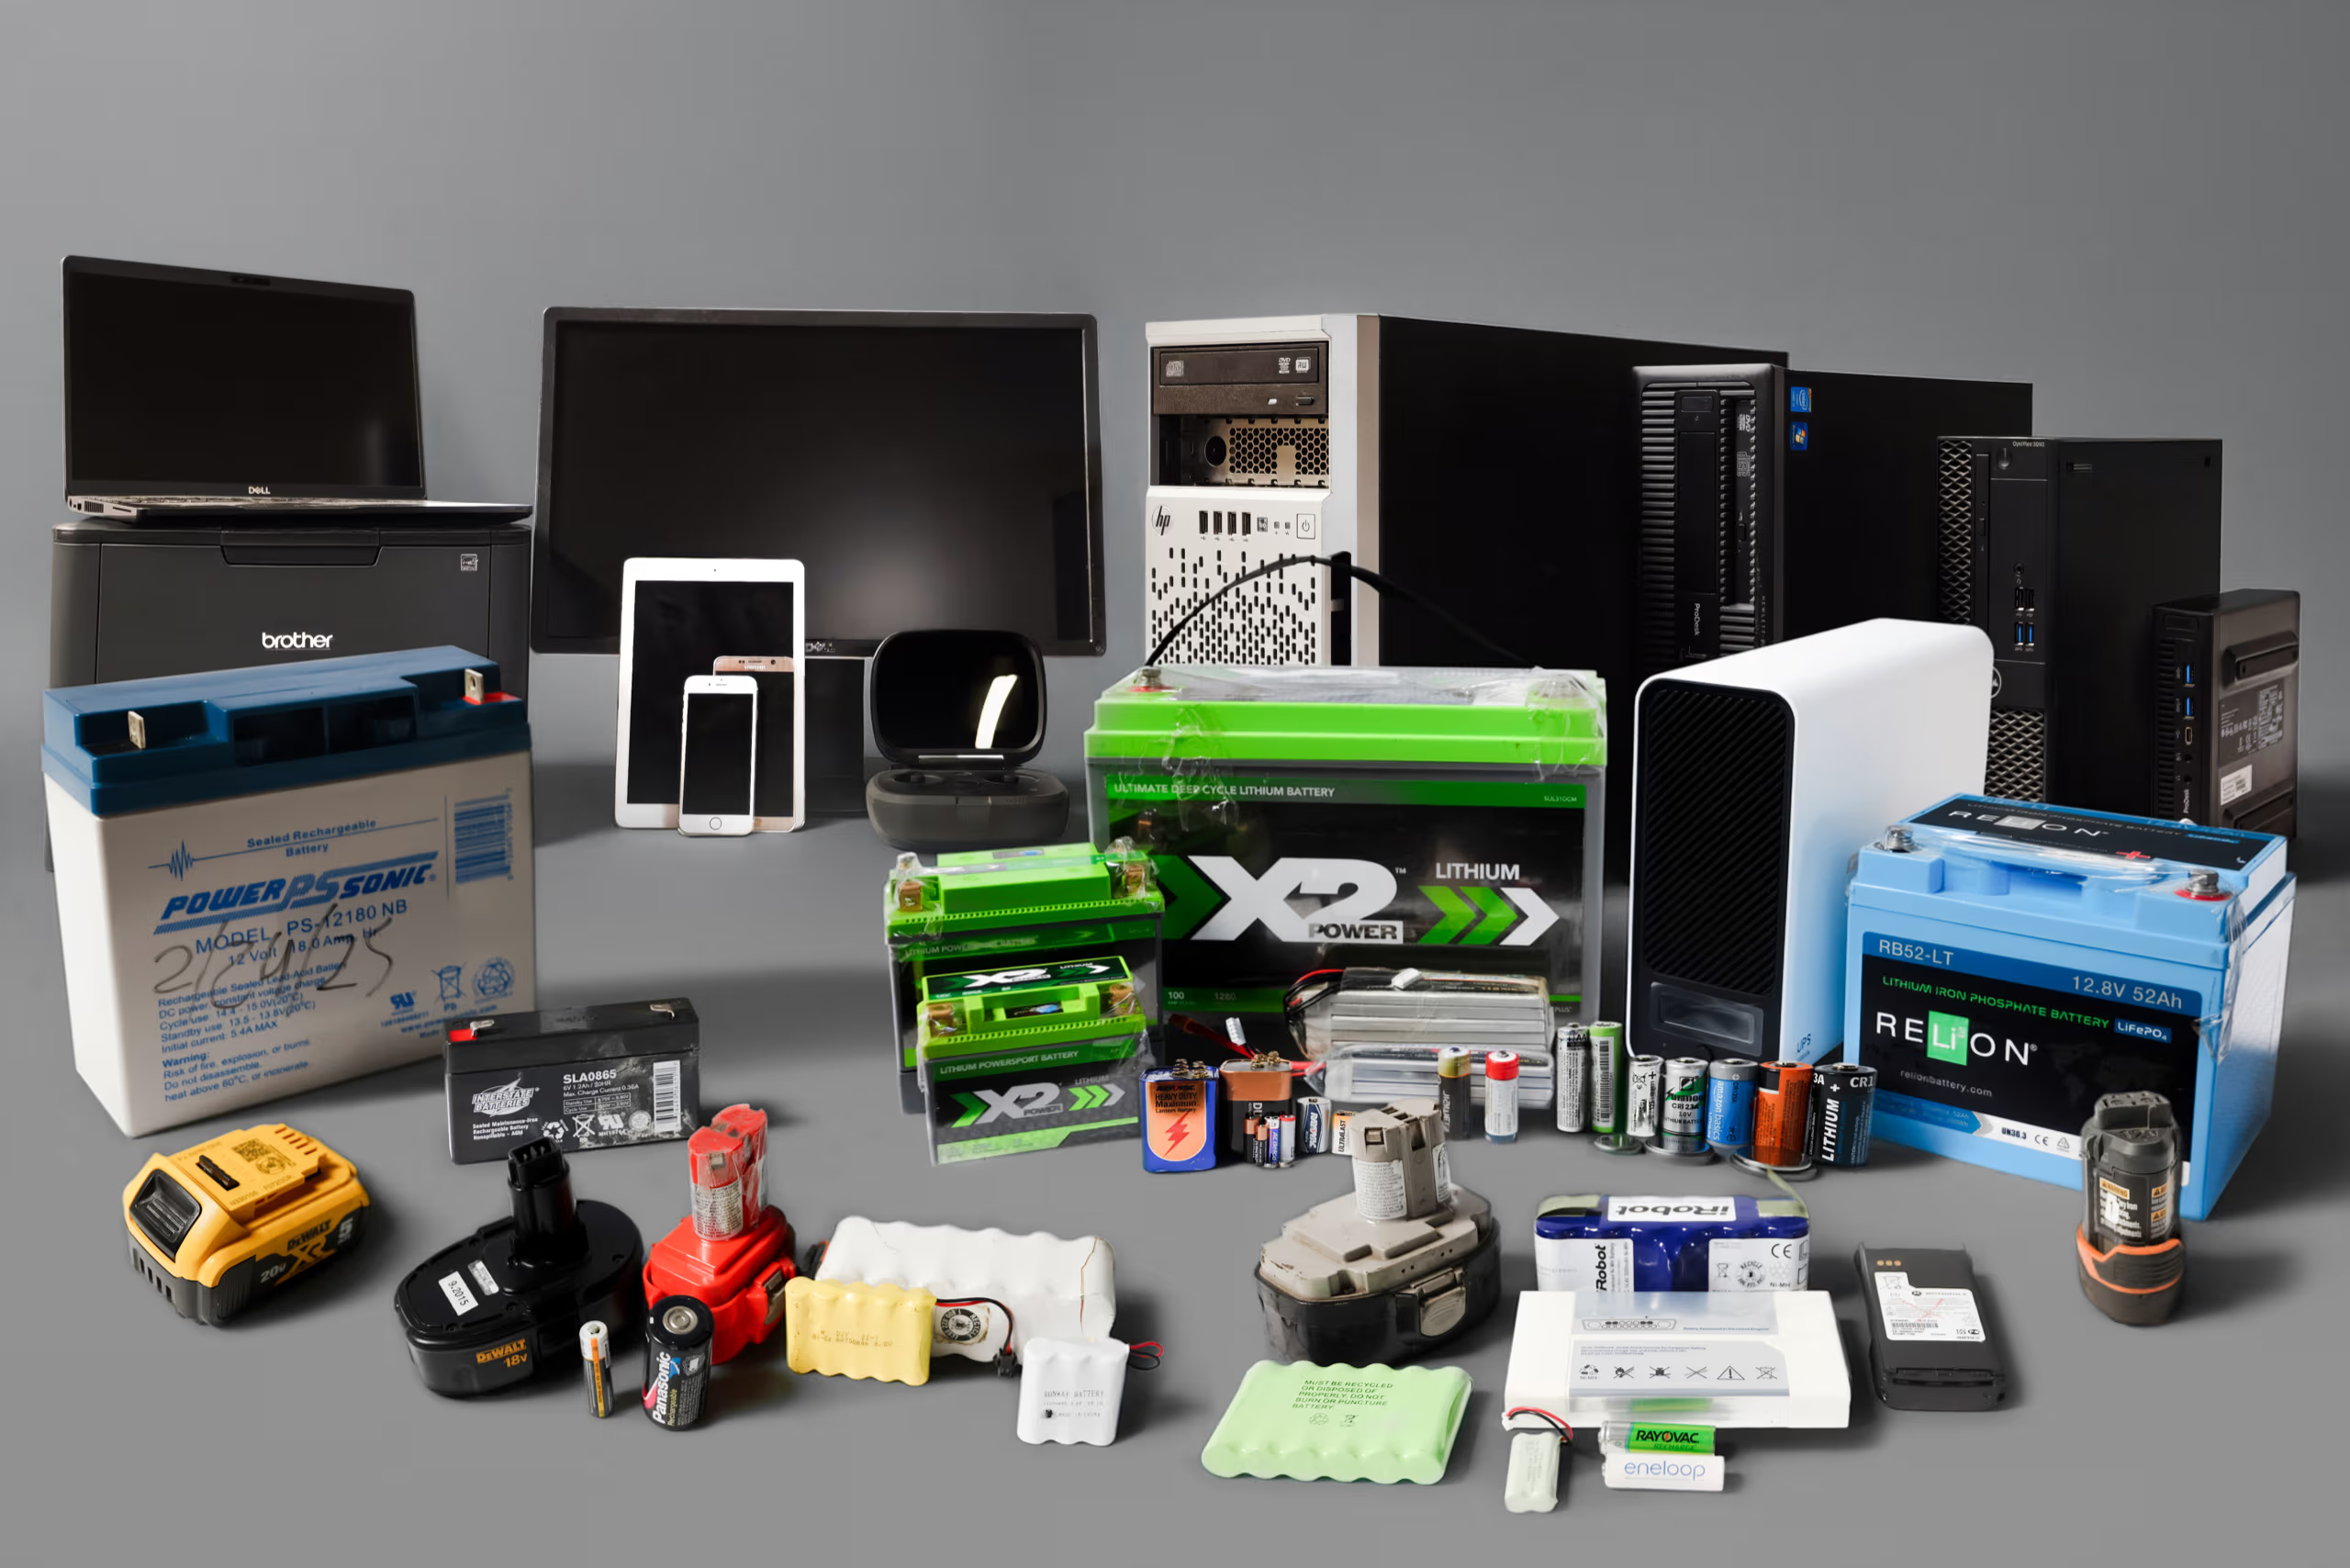

Simplify your compliance and disposal process with bundled recycling services that handle both electronic devices and batteries in one streamlined solution.
Our scheduled, route-based pickups cover all major regions of California—ensuring efficient, on-time service no matter where you operate.
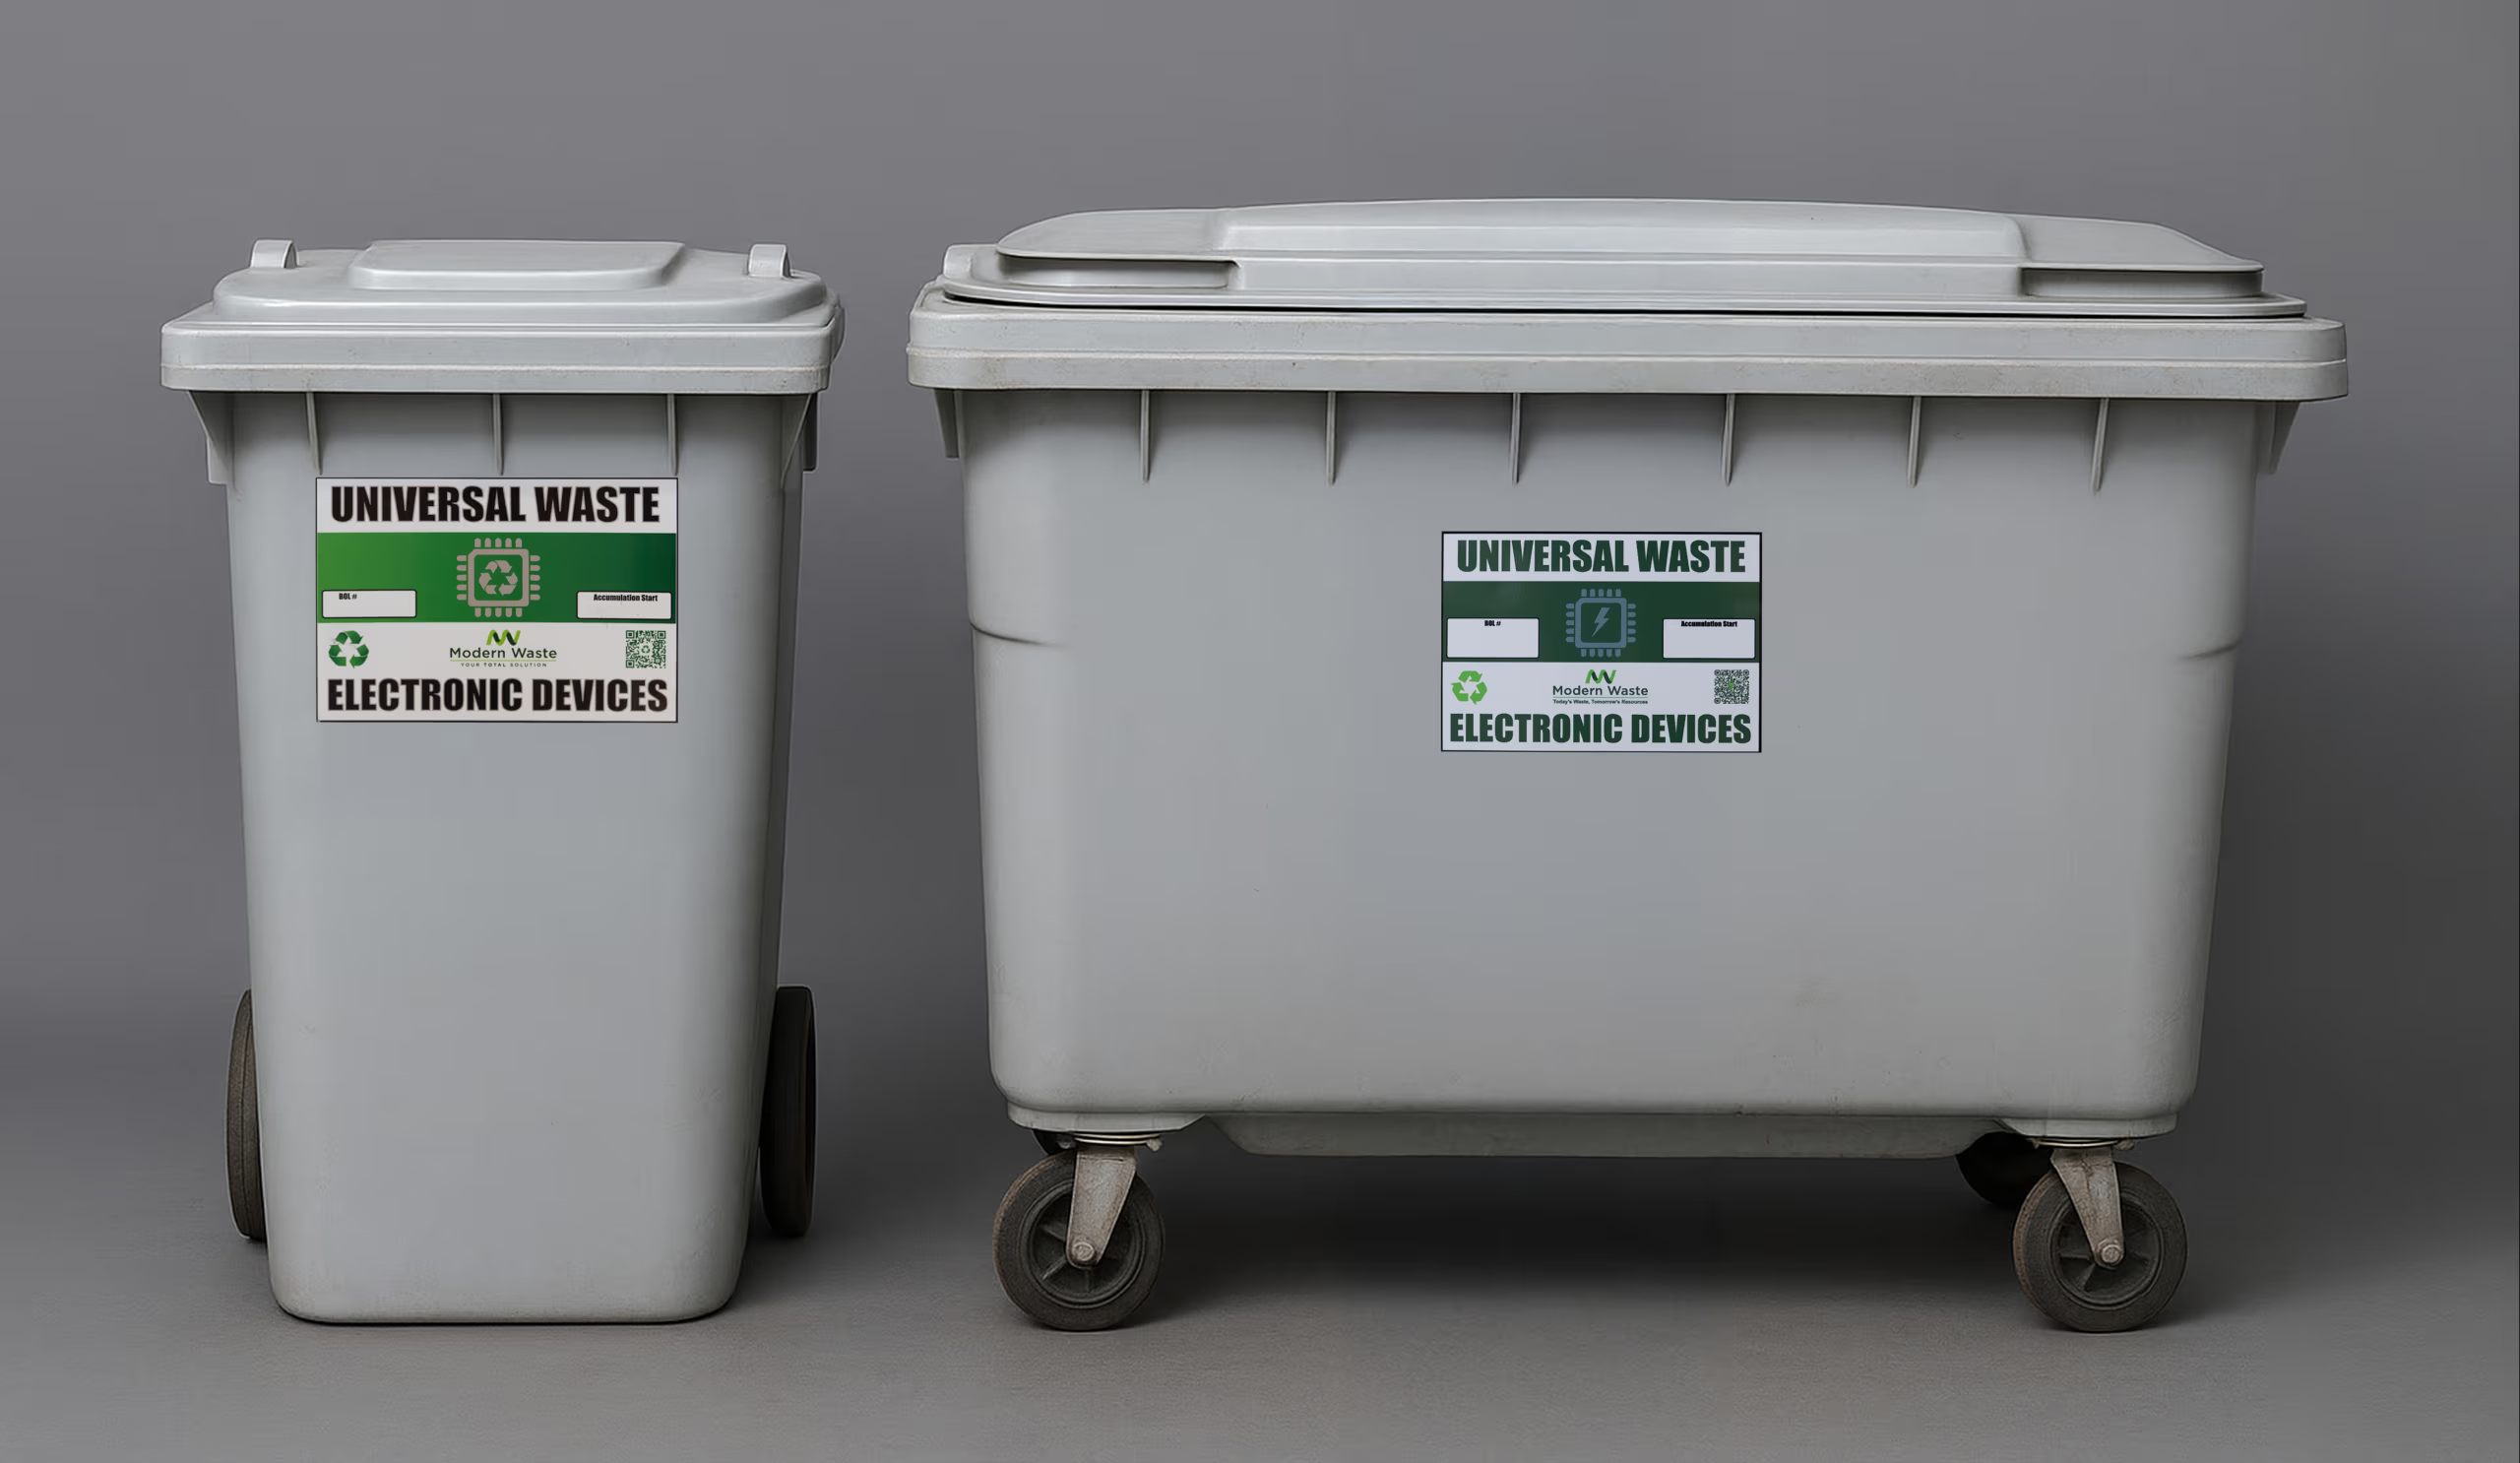
We provide clearly labeled, tamper-resistant containers to ensure safe and compliant collection of electronic waste and batteries at your location.
Modern Waste Solutions has served businesses and communities across California with dependable, environmentally responsible recycling solutions for over two decades.
We adhere to all California and federal regulations, ensuring your electronic and battery waste is managed with complete transparency and environmental responsibility.

Reviews
A little bit off the beaten track in Natomas, but Modern Waste quickly and efficiently helped me recycle my broken Lithium Iron Phosphate batteries at a reasonable $/lb fee (Sac county e-waste will not accept these items). Ramiro and Vincent were very friendly and helpful.

Chris was awesome! He came in and picked up all of the e-waste we had ready for him. He was polite and professional throughout the entire process. He handled the equipment with care, including the site equipment that was already in place. I am very happy with his service and appreciate the great job he did.

Aaron and Vincent were awesome, excellent customer service!

Great guys, excellent customer service, highly recommend!

Polite, quick and easy.

Chris from modern waste was the most outstanding respectful person I ever met my life when he was done he offered to sweep the floors. He offered so much even though he was limited on time he went out of his way and he’s over beyond best guy I ever met thank you so much for your service services Dan ITG.

Data center decommissioning is a controlled change project that retires workloads, infrastructure, and records without interrupting systems that must remain live. Here is the full process, from go/no-go to final reconciliation.
A mature ITAD program connects asset ownership, data security, environmental compliance, logistics, financial recovery, and reconciliation. Here is how the process works, what it costs, and how to evaluate a provider.
IT equipment liquidation converts marketable retired assets into documented financial recovery while routing nonmarketable equipment to responsible recycling. Here is how to decide which path fits each asset.